Overview
Understand what this system does, why it matters, and what you'll walk away with.
Detect and manage risk from the people already inside the organization — fairly, and before it escalates.
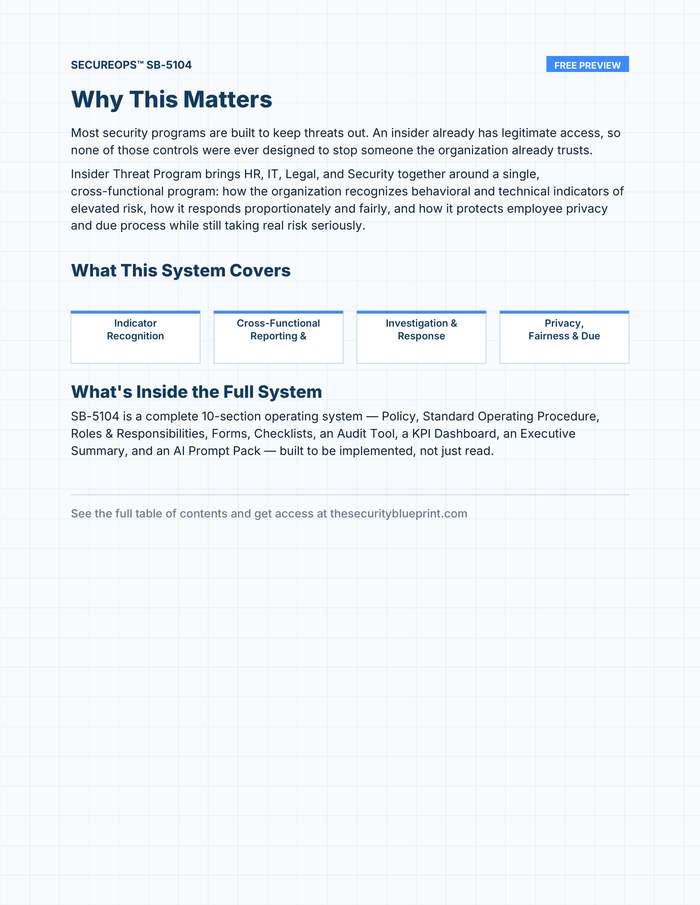
Most security programs are built to keep threats out. An insider already has legitimate access, so none of those controls were ever designed to stop someone the organization already trusts.
Insider Threat Program brings HR, IT, Legal, and Security together around a single, cross-functional program: how the organization recognizes behavioral and technical indicators of elevated risk, how it responds proportionately and fairly, and how it protects employee privacy and due process while still taking real risk seriously.
Every SecureOps™ system ships pre-populated with real sample data, not blank placeholders, so you can see exactly how the finished document reads before you customize it for your facility.
Two real pages from the free preview. No download or new tab required.
19 pages · 10 sections · one editable .docx file
See it for yourself — real excerpts from the document
One of three checklists inside — this is what happens before any concern becomes a case.
↑ Real sample content from the delivered document. Sections 02–10 unlock after purchase.
Every section builds on the last — policy, procedure, forms, audits, and reporting, working together as one system. Preview it now: Overview is open below.
Understand what this system does, why it matters, and what you'll walk away with.
The organization's official position on insider threat management.
A repeatable process from indicator recognition through resolution.
Who does what, so insider risk is never assessed by one function acting alone.
Ready-to-use forms that put the Policy and SOP into practice.
Fast, scannable versions of the SOP for day-to-day use.
Verify triage, privacy safeguards, and documentation are all operating as designed.
Track the health of the system over time.
One page, built to forward to leadership.
Ready-to-copy prompts you paste into an AI assistant to adapt this system to your facility.
Instant digital delivery — .docx file, licensed for your whole organization, no resale. SB-5104.